Topics in this domain
- IT Governance vs. IT Management
- Board and Senior Management Roles
- IT Steering Committee
- IT Strategy and Business Alignment
- Balanced Scorecard
- COBIT
- ITIL
- ISO 27001/27002
- COSO: ERM and Internal Control
- Policies, Standards, Procedures, Guidelines
- IT Organizational Structure and Key Roles
- Segregation of Duties in IT
- Enterprise Architecture (Zachman, TOGAF)
- Risk Management Process
- Qualitative vs. Quantitative Risk Assessment
- Risk Responses: Mitigate, Transfer, Avoid, Accept
- Risk Appetite and Residual Risk
- Maturity Models (CMMI)
- KPIs and KGIs
- Outsourcing: Benefits and Risks
- Vendor Selection, Contracts, SLAs, Right to Audit
- Cloud and Offshore Governance
- Portfolio and Resource Management
- HR: Hiring, Training, Termination
- Legal and Regulatory Compliance
- Quality Management
Legal and Regulatory Compliance
Rules from every direction
Organisations face rules from many sources: privacy laws, financial regulations, industry rules, and contracts with customers and suppliers. Breaking them can mean fines, lawsuits, or losing the right to operate.
Think of running a restaurant. Food safety laws, licensing rules, employment law, fire regulations, and the terms of your lease all apply at once. A good restaurant keeps a list, assigns someone to each, and checks regularly. It doesn’t wait for the inspector to turn up.
Management is responsible for knowing which rules apply and for complying with them. Internal audit checks how well that’s done.
A compliance process
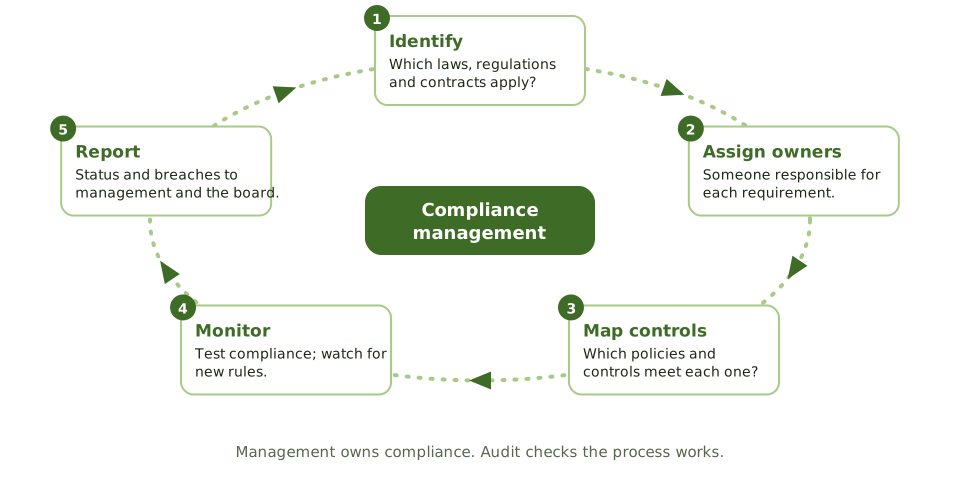
- Identify the requirements: laws in each country, sector rules, contracts, standards the organisation has signed up to.
- Assign owners for each requirement.
- Map policies and controls to each requirement. One control often covers several.
- Monitor compliance through testing and self-assessment, and track regulatory change.
- Report status and breaches to management and the board.
- Train staff on the rules that apply to their roles.
IT-related obligations
| Area | Examples |
|---|---|
| Privacy and data protection | GDPR, national privacy laws, health data rules |
| Financial reporting | Sarbanes-Oxley in the US, and equivalents elsewhere |
| Sector regulation | Banking regulators’ IT and outsourcing rules, health data, operational resilience rules |
| Payment cards | PCI DSS, enforced through contracts |
| Intellectual property | Software licensing and copyright |
| Record retention | Tax, employment and industry rules on how long to keep records and how to destroy them |
| Electronic evidence | Duties to preserve and produce records in legal cases |
| Cross-border data | Limits on moving personal data abroad |
The auditor’s approach
When auditing compliance, the first step is identifying which requirements apply to the organisation and the area being audited. Then the auditor:
- reviews how management identifies and tracks requirements
- checks policies and procedures reflect current rules
- tests the key controls
- consults legal counsel on interpretation, because the auditor isn’t a lawyer
- reports non-compliance to the right level of management, and to the audit committee if significant
Example. A new HR system stores employees’ health information, which privacy law treats as especially sensitive. No privacy impact assessment was done, and the compliance team didn’t know the system existed. The finding: the compliance process doesn’t catch new systems handling regulated data.
How the exam asks about it
| If the question asks… | The answer is usually… |
|---|---|
| First step in a compliance audit | Identify the laws and regulations that apply |
| Who is responsible for compliance? | Management |
| The auditor is unsure how a law applies | Consult legal counsel |
| Control to keep policies in line with new regulation | A process for tracking regulatory change |
| Is PCI DSS a legal requirement? | It’s a contractual obligation, treated as a compliance requirement |
In short
- Management is responsible for knowing which laws and regulations apply and for complying with them.
- A compliance process needs a list of requirements, owners, controls mapped to each requirement, monitoring and reporting.
- IT-related obligations include privacy, financial reporting (such as SOX), sector rules, card data (PCI DSS), licensing and record retention.
- The auditor's first step is identifying which requirements apply, then checking the organisation has a process to meet them.
- The auditor isn't a lawyer; legal questions go to legal counsel.
- Regulatory changes must be tracked so policies and controls stay current.
Exam traps
- The auditor's first step is understanding which requirements apply, not testing controls.
- Compliance is management's responsibility, not internal audit's.
- On suspecting an illegal act, the auditor reports it internally; they don't decide the legal outcome.
- Contractual obligations, like PCI DSS through card agreements, count as compliance requirements even though they aren't laws.
Slides
Click the slide and use the arrow keys. F toggles full screen.
Rules from every direction
Organisations face rules from many sources: privacy laws, financial regulations, industry rules, contracts with customers and suppliers. Breaking them can mean fines, lawsuits or losing the right to operate.
Keeping track of them all needs a process, not good intentions.