Topics in this domain
- IT Governance vs. IT Management
- Board and Senior Management Roles
- IT Steering Committee
- IT Strategy and Business Alignment
- Balanced Scorecard
- COBIT
- ITIL
- ISO 27001/27002
- COSO: ERM and Internal Control
- Policies, Standards, Procedures, Guidelines
- IT Organizational Structure and Key Roles
- Segregation of Duties in IT
- Enterprise Architecture (Zachman, TOGAF)
- Risk Management Process
- Qualitative vs. Quantitative Risk Assessment
- Risk Responses: Mitigate, Transfer, Avoid, Accept
- Risk Appetite and Residual Risk
- Maturity Models (CMMI)
- KPIs and KGIs
- Outsourcing: Benefits and Risks
- Vendor Selection, Contracts, SLAs, Right to Audit
- Cloud and Offshore Governance
- Portfolio and Resource Management
- HR: Hiring, Training, Termination
- Legal and Regulatory Compliance
- Quality Management
Risk Responses: Mitigate, Transfer, Avoid, Accept
Four ways to respond
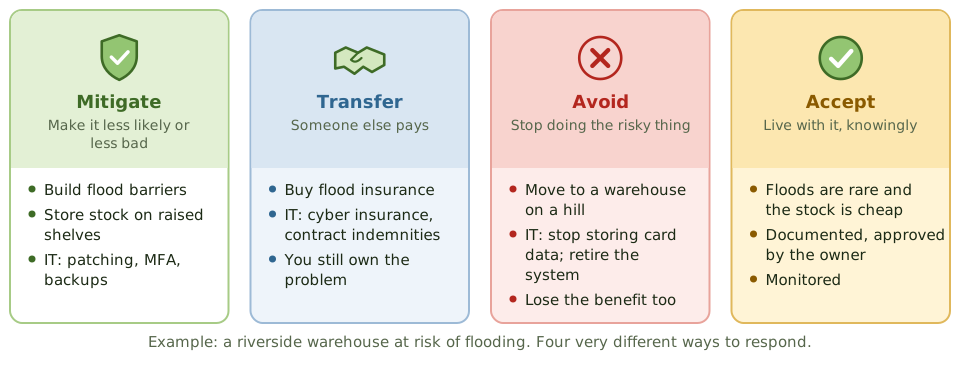
Once a risk has been assessed, there are only four basic responses. A riverside warehouse at risk of flooding shows them clearly.
| Response | What it means | IT examples | When it fits |
|---|---|---|---|
| Mitigate (reduce) | Put in controls to make the risk less likely or less damaging | MFA, encryption, patching, redundant systems, training | Risk is above appetite and controls are cost-effective |
| Transfer (share) | Shift the financial consequences to someone else | Cyber insurance, contract indemnities, outsourcing with penalties | High-impact, low-likelihood events |
| Avoid | Stop, or don’t start, the activity | Withdraw a product, stop storing card data, retire a legacy system | Risk is unacceptable and can’t be treated cost-effectively |
| Accept | Knowingly live with the risk | Document the decision; monitor | Within appetite, or treatment costs more than it saves |
Responses can be combined: mitigate to make an event less likely, then insure against what’s left.
Transfer has limits
Insurance and contracts move money. They don’t move:
- accountability: you’re still responsible for your data and your customers
- reputational damage
- regulatory duties: fines often can’t be insured, and regulators hold the organisation accountable
The same goes for outsourcing: you can outsource the work, not the accountability.
Acceptance is a decision, not a shrug
Accepting a risk is perfectly legitimate when it’s:
- informed: the risk has been assessed and understood
- within appetite, or approved at a higher level (often senior management or the board) if it’s beyond it
- documented, with the owner, the reason and a review date
- monitored, so changes trigger a fresh look
Ignoring a risk, or not knowing about it, isn’t acceptance. And IT staff can’t accept business risks: the business risk owner does.
Example. A legacy system can’t support MFA. Replacing it costs 2 million and takes 18 months. Management puts it behind a VPN with MFA and adds extra monitoring (mitigate), and the business owner formally accepts the remaining risk until the replacement, reviewing it every quarter (accept).
How the exam asks about it
| If the question asks… | The answer is usually… |
|---|---|
| Buying cyber insurance is an example of… | Risk transfer |
| Does insurance transfer responsibility? | No; only financial impact |
| Stopping an activity because the risk is too high | Avoidance |
| Who can accept residual risk? | The business risk owner / senior management |
| Requirement for valid risk acceptance | An informed, documented decision at the right level |
| Response when the risk is within appetite | Acceptance (with monitoring) |
In short
- Mitigate: reduce how likely or how bad the risk is, with controls.
- Transfer: shift the financial impact to someone else, through insurance or contracts.
- Avoid: stop doing the activity that creates the risk.
- Accept: knowingly live with the risk, because it's within appetite or fixing it costs more than it saves.
- Transferring risk moves money, not accountability; reputational and regulatory impact stay with you.
- Accepting a risk is a documented decision by someone with authority, not just ignoring it.
Exam traps
- Insurance transfers financial loss, not responsibility or reputational damage.
- Ignoring a risk is not acceptance; acceptance is informed, documented and approved.
- Outsourcing a process doesn't transfer accountability for it.
- Avoidance is the only response that removes the risk completely, and you lose the activity's benefits too.
- IT staff can't accept business risk on the business's behalf.
Slides
Click the slide and use the arrow keys. F toggles full screen.
Four ways to respond
Once a risk is assessed, there are only four basic responses. A riverside warehouse at risk of flooding shows them clearly.