Topics in this domain
- IT Governance vs. IT Management
- Board and Senior Management Roles
- IT Steering Committee
- IT Strategy and Business Alignment
- Balanced Scorecard
- COBIT
- ITIL
- ISO 27001/27002
- COSO: ERM and Internal Control
- Policies, Standards, Procedures, Guidelines
- IT Organizational Structure and Key Roles
- Segregation of Duties in IT
- Enterprise Architecture (Zachman, TOGAF)
- Risk Management Process
- Qualitative vs. Quantitative Risk Assessment
- Risk Responses: Mitigate, Transfer, Avoid, Accept
- Risk Appetite and Residual Risk
- Maturity Models (CMMI)
- KPIs and KGIs
- Outsourcing: Benefits and Risks
- Vendor Selection, Contracts, SLAs, Right to Audit
- Cloud and Offshore Governance
- Portfolio and Resource Management
- HR: Hiring, Training, Termination
- Legal and Regulatory Compliance
- Quality Management
Risk Management Process
What risk actually is
“Risk” gets used loosely. In risk management it has a precise shape: something valuable (an asset), something that could harm it (a threat), and a weakness that would let the harm happen (a vulnerability).
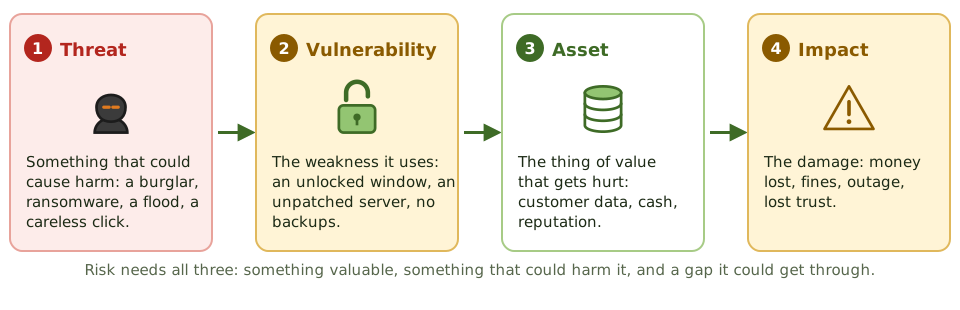
Think of your home. The asset is your laptop. The threat is a burglar. The vulnerability is an open window. The impact is losing the laptop and everything on it. Close the window (fix the vulnerability) or move to a safer neighbourhood (reduce the threat) and the risk drops.
A threat with no vulnerability to use, or a vulnerability no threat can reach, poses little risk. Controls work by reducing the likelihood (closing gaps, blocking threats) or reducing the impact (backups, insurance).
- Inherent risk is the level before any controls.
- Residual risk is what’s left after controls.
The cycle
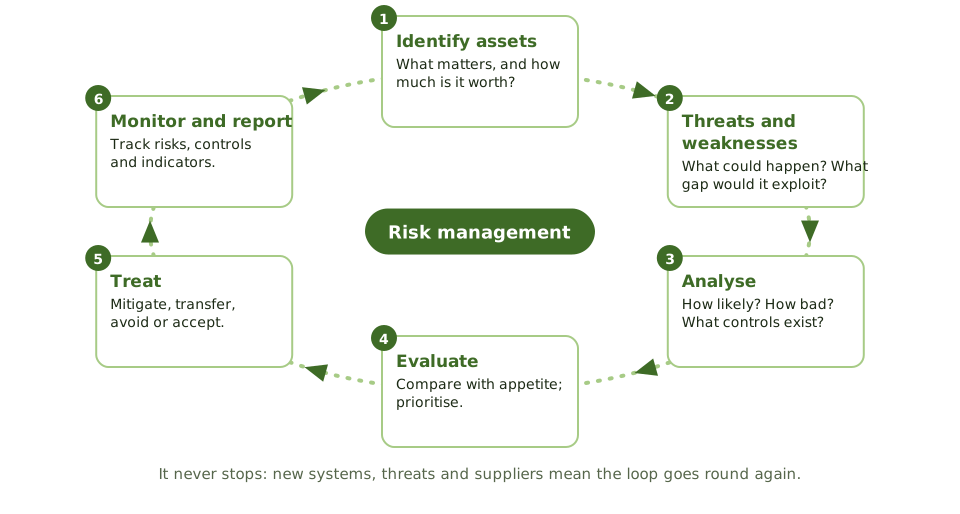
| Step | What happens |
|---|---|
| 1. Set the context | Goals, scope, risk criteria and appetite, stakeholders |
| 2. Identify assets | Information, systems, processes, people; their value and owners |
| 3. Identify threats and vulnerabilities | What could happen, and what weakness it would exploit |
| 4. Analyse | How likely, how bad, considering existing controls |
| 5. Evaluate | Compare with appetite; prioritise |
| 6. Treat | Mitigate, transfer, avoid or accept |
| 7. Monitor and review | Track risks and controls, watch key risk indicators, reassess after change |
| Throughout | Communicate, and record everything in a risk register |
When the exam asks what comes first in a risk assessment, the answer is usually identifying the assets (and their value or criticality). You can’t prioritise threats to things you haven’t listed.
Who does what
- The board sets risk appetite.
- Risk owners in the business are accountable for their risks. They decide on treatment and accept the residual risk.
- The risk function provides the framework and methods, facilitates assessments, and pulls the picture together.
- Control owners run the controls.
- Internal audit gives independent assurance that risk management works. It doesn’t own or run it.
This is often called the three lines model: management (first line), risk and compliance (second line), internal audit (third line).
The risk register
A risk register records each risk with its owner, ratings, controls, treatment plan and status:
| Field | Example |
|---|---|
| Risk | Ransomware encrypts file servers |
| Owner | COO |
| Inherent rating | High |
| Controls | Endpoint protection, offline backups, patching |
| Residual rating | Medium |
| Treatment and date | Immutable backups by Q3 |
Keep it current
Risks change with new systems, threats, suppliers and laws. Assessments should be repeated regularly and after significant change. Key risk indicators give early warning in between.
Example. A company assessed IT risk in January. In June it moved customer data to a cloud service. Without a new assessment, the risk register still talks about on-premises databases and says nothing about the provider, its access model or where the data now lives.
How the exam asks about it
| If the question asks… | The answer is usually… |
|---|---|
| The first step in a risk assessment | Identify and value assets |
| Who accepts residual risk? | The business risk owner (senior management) |
| What risk is a function of | Threats, vulnerabilities and impact on assets |
| When to reassess risk | Regularly and after significant change |
| Internal audit’s role in risk management | Independent assurance over the process |
In short
- Risk management starts with context and assets, then threats and vulnerabilities, then analysing likelihood and impact.
- Risk exists when a threat can exploit a vulnerability to harm an asset.
- Risk evaluation compares each risk with the organisation's appetite to decide what to do.
- Treatment options are mitigate, transfer, avoid or accept; residual risk must be within appetite and accepted by the risk owner.
- Risk management is continuous: risks are monitored and reassessed, especially after changes.
- Business risk owners are accountable for their risks; the risk function facilitates; internal audit gives independent assurance.
- A risk register records each risk, its owner, rating, treatment and status.
Exam traps
- The first step in a risk assessment is identifying and valuing assets, not picking controls.
- A vulnerability no threat can exploit (or a threat with nothing to exploit) doesn't create much risk.
- IT doesn't own business risks. The business owner accepts residual risk.
- An annual risk assessment isn't enough after a big change; reassess when things change.
- Audit evaluates the risk management process; it doesn't run it.
Slides
Click the slide and use the arrow keys. F toggles full screen.
What risk actually is
'Risk' gets used loosely. In risk management it has a precise shape: something valuable, something that could harm it, and a weakness that would let the harm happen.
Take away any one of those and the risk shrinks. That's what controls do.
The risk management cycle