Topics in this domain
- Security Governance and Roles
- Data Classification and Ownership
- Security Policies
- Privacy Principles and GDPR
- Identity Management
- Authentication Factors
- Biometrics
- Access Models: DAC, MAC, RBAC
- Logical and Privileged Access
- Cryptography Basics
- Symmetric Encryption
- Asymmetric Encryption
- Hashing and Integrity
- Digital Signatures
- PKI and Certificates
- Firewalls
- IDS/IPS
- VPN, SSL/TLS, IPsec
- Wireless Security
- Endpoint and Mobile (BYOD)
- Cloud and Virtualization Security
- Physical Access Controls
- Environmental Controls: Fire, Power, HVAC
- Social Engineering
- Malware
- Network Attacks: DoS, Spoofing, Sniffing
- Application Attacks: SQLi, XSS
- Vulnerability Management and Pen Testing
- Incident Response
- Digital Forensics and Chain of Custody
- Security Awareness Training
- Logging, SIEM, and Auditing Security
IDS/IPS
Alarm or guard?
A burglar alarm tells you someone has broken in. A guard at the door stops them getting in at all. Both are useless if nobody answers the alarm, or the guard falls asleep.
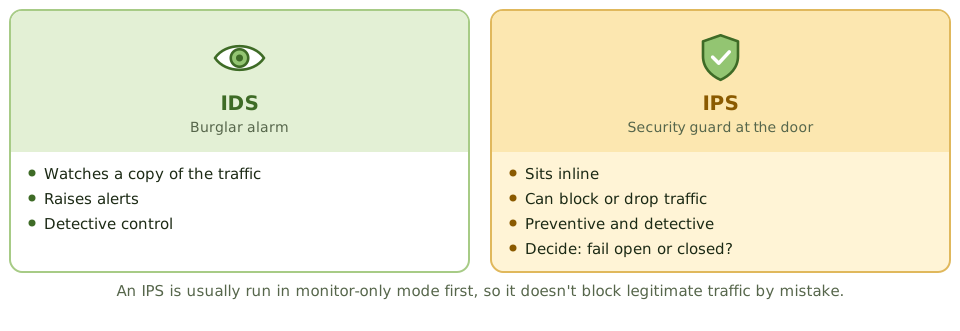
- An intrusion detection system (IDS) watches activity and raises alerts on possible attacks. It’s a detective control.
- An intrusion prevention system (IPS) sits inline and can block or drop malicious traffic automatically. It’s preventive as well as detective.
A badly tuned IPS can block legitimate traffic, so it’s usually run in monitor-only mode first, and switched to blocking once false alarms are understood. If the IPS itself fails, it either lets everything through (fails open) or blocks everything (fails closed); that’s a decision to make in advance.
Network or host?
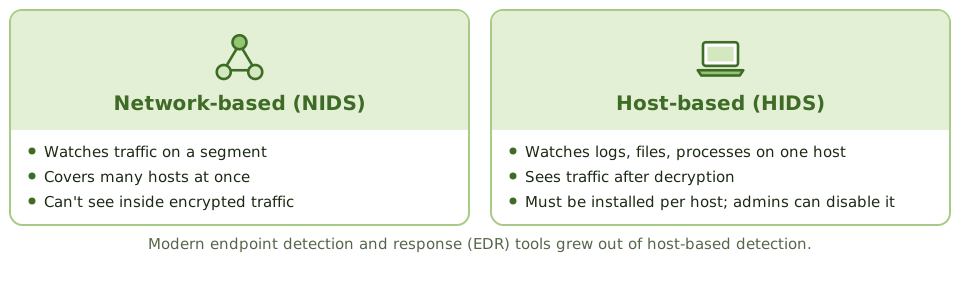
| Type | Watches | Strengths | Limitations |
|---|---|---|---|
| Network-based (NIDS) | Traffic on a network segment, via a span port or tap | Covers many hosts; invisible to attackers | Can’t see inside encrypted traffic; may miss activity on the host |
| Host-based (HIDS) | Logs, processes, file integrity and settings on one host | Sees what really happens, after decryption | Installed and managed per host; an attacker with admin rights can switch it off |
Modern endpoint detection and response (EDR) tools grew out of host-based detection.
How it spots attacks
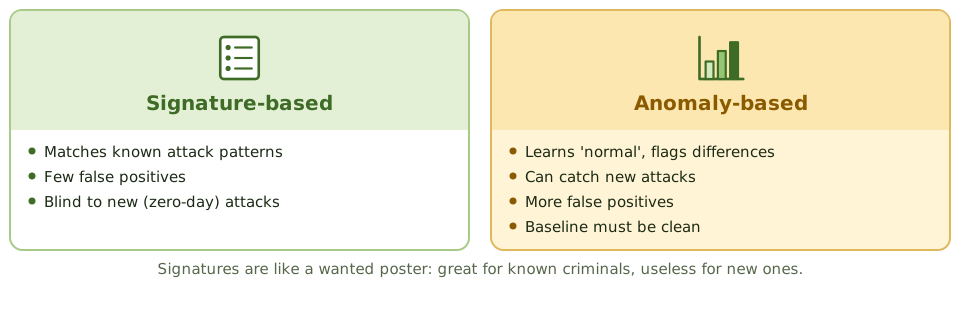
| Method | How it works |
|---|---|
| Signature-based | Compares activity with a database of known attack patterns. Accurate for known attacks, but blind to new (zero-day) attacks until a signature exists |
| Statistical / anomaly-based | Learns what normal looks like and flags anything different. Can catch new attacks, but produces more false positives |
| Neural network / machine learning | Learns patterns from data; like anomaly detection, but adapts |
Anomaly detection needs a clean baseline. A baseline taken during an attack learns the attack as “normal”.
Two kinds of error
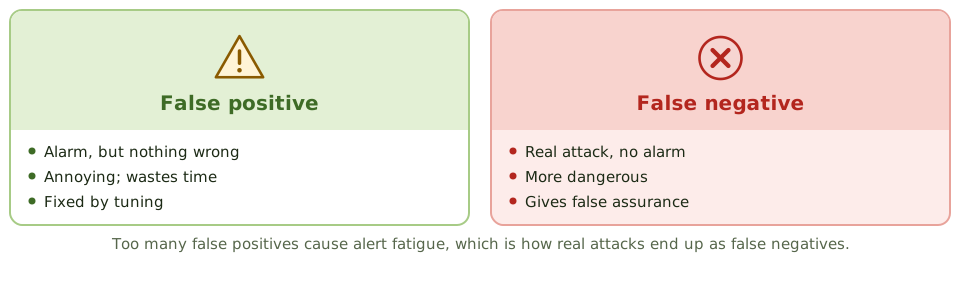
- False positive: an alert when nothing is wrong. Too many cause alert fatigue.
- False negative: a real attack with no alert. More dangerous, because it gives false assurance.
Tuning adjusts signatures and thresholds to the environment, cutting false positives without creating false negatives.
Example. An IDS generates 30,000 alerts a day, almost all false positives from an untuned rule set. The security team stopped reviewing them months ago, and a real alert about data being stolen was buried among them. The finding: without tuning and monitoring, the control is ineffective.
Placement
- at the perimeter, behind the external firewall, to see attacks that get through
- in front of critical segments (data centre, payment environment)
- on critical hosts (HIDS)
- in cloud environments, using the provider’s own tools
Honeypots
A honeypot is a decoy system built to attract attackers. It has no legitimate use, so any interaction with it is suspicious. It gives early warning and shows how attackers work. A honeynet is a network of honeypots. Both must be isolated so attackers can’t use them to reach real systems.
Someone has to answer the alarm
An IDS nobody watches protects nothing. Alerts should feed a SIEM or security operations centre, with defined triage and response procedures.
How the exam asks about it
| If the question asks… | The answer is usually… |
|---|---|
| Detection method that can find new attacks | Anomaly / statistical-based |
| Detection method with fewest false positives for known attacks | Signature-based |
| More dangerous IDS error | False negative |
| Main difference between IDS and IPS | IPS is inline and can block |
| Decoy system to attract attackers | Honeypot |
| What makes an IDS effective | Tuning plus timely monitoring and response |
In short
- An IDS detects and alerts on suspicious activity; an IPS sits inline and can block it.
- Network-based IDS (NIDS) monitors traffic on a segment; host-based IDS (HIDS) monitors activity and files on a single host.
- Signature-based detection matches known attack patterns: accurate for known attacks, blind to new ones.
- Anomaly (statistical or behaviour-based) detection flags deviations from normal: can find new attacks but produces more false positives.
- A false positive is an alert on legitimate activity; a false negative is a missed attack, which is more dangerous.
- An IPS can block legitimate traffic if poorly tuned, so it's usually introduced in monitoring mode first.
- Detection is useless without monitoring and response: alerts must be reviewed and acted on.
Exam traps
- Signature-based IDS can't detect zero-day attacks without a signature.
- Anomaly-based IDS needs a baseline of normal activity; a baseline taken during an attack treats the attack as normal.
- Encrypted traffic can hide attacks from a network IDS unless decrypted or monitored at the host.
- An IPS failure can disrupt traffic; decide whether it fails open or closed.
- Too many false positives lead to alert fatigue and real attacks being ignored.
Slides
Click the slide and use the arrow keys. F toggles full screen.
Alarm or guard?
A burglar alarm tells you someone's broken in. A guard at the door stops them coming in at all. Both are useless if nobody answers the alarm or the guard falls asleep.
An intrusion detection system (IDS) is the alarm. An intrusion prevention system (IPS) is the guard.
Network or host?
How it spots attacks
Two kinds of error