Topics in this domain
- Security Governance and Roles
- Data Classification and Ownership
- Security Policies
- Privacy Principles and GDPR
- Identity Management
- Authentication Factors
- Biometrics
- Access Models: DAC, MAC, RBAC
- Logical and Privileged Access
- Cryptography Basics
- Symmetric Encryption
- Asymmetric Encryption
- Hashing and Integrity
- Digital Signatures
- PKI and Certificates
- Firewalls
- IDS/IPS
- VPN, SSL/TLS, IPsec
- Wireless Security
- Endpoint and Mobile (BYOD)
- Cloud and Virtualization Security
- Physical Access Controls
- Environmental Controls: Fire, Power, HVAC
- Social Engineering
- Malware
- Network Attacks: DoS, Spoofing, Sniffing
- Application Attacks: SQLi, XSS
- Vulnerability Management and Pen Testing
- Incident Response
- Digital Forensics and Chain of Custody
- Security Awareness Training
- Logging, SIEM, and Auditing Security
Privacy Principles and GDPR
Privacy isn’t just security
A doctor’s receptionist who locks your medical file in a safe has kept it secure. If they also asked for your salary, and passed your details to a marketing firm, they’ve broken your privacy, however good the safe was.
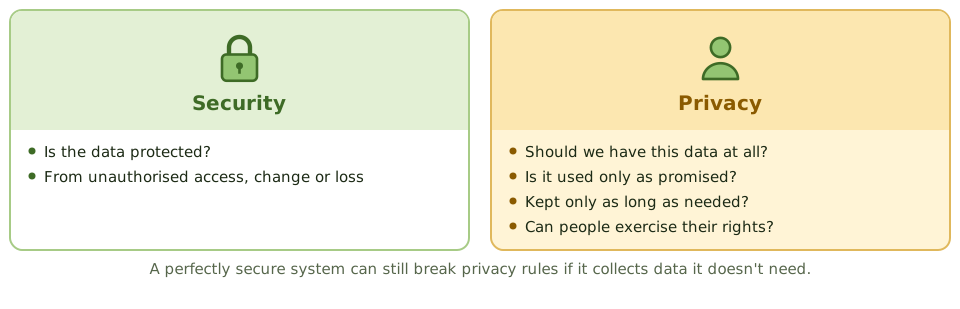
Privacy is about how personal information is collected, used, shared and kept, and the rights of the people it’s about. Security protects information from unauthorised access, change or loss. Security supports privacy, but a perfectly secure system can still breach privacy if it collects data it doesn’t need, or uses it for purposes nobody was told about.
The seven principles
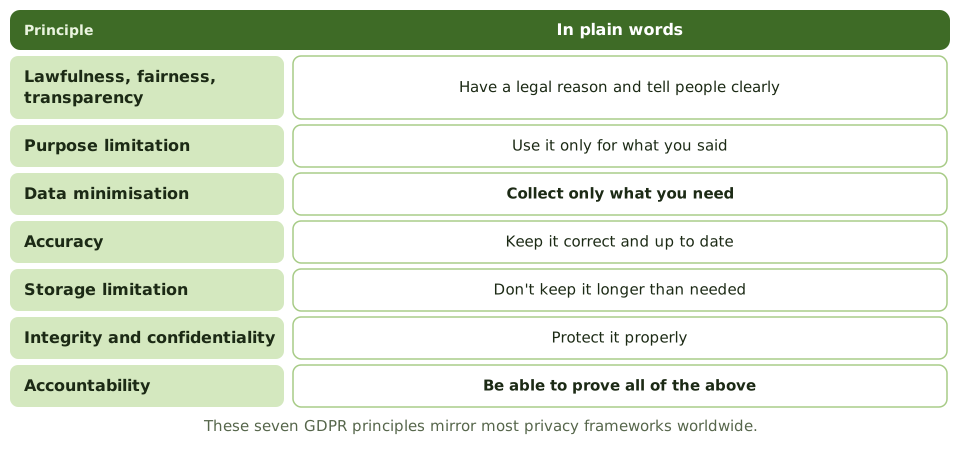
These GDPR principles mirror most privacy frameworks, such as the OECD guidelines:
| Principle | Meaning |
|---|---|
| Lawfulness, fairness, transparency | Have a legal basis for processing; tell people clearly |
| Purpose limitation | Collect for specified purposes; don’t reuse it for something incompatible |
| Data minimisation | Only what’s adequate, relevant and necessary |
| Accuracy | Keep it accurate and up to date |
| Storage limitation | Don’t keep it longer than necessary |
| Integrity and confidentiality | Protect it with appropriate security |
| Accountability | The controller can prove compliance |
GDPR essentials
- Scope: applies to processing personal data of people in the EU, including by organisations outside the EU that offer them goods or services or monitor them.
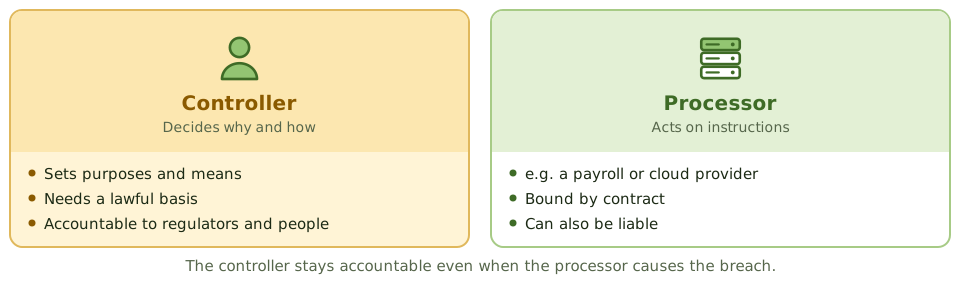
- Roles: the controller decides the purposes and means; the processor acts on the controller’s instructions under a contract. The controller remains accountable, even if the processor causes the breach (the processor may be liable too).
- Lawful bases: consent, contract, legal obligation, vital interests, public task, legitimate interests.
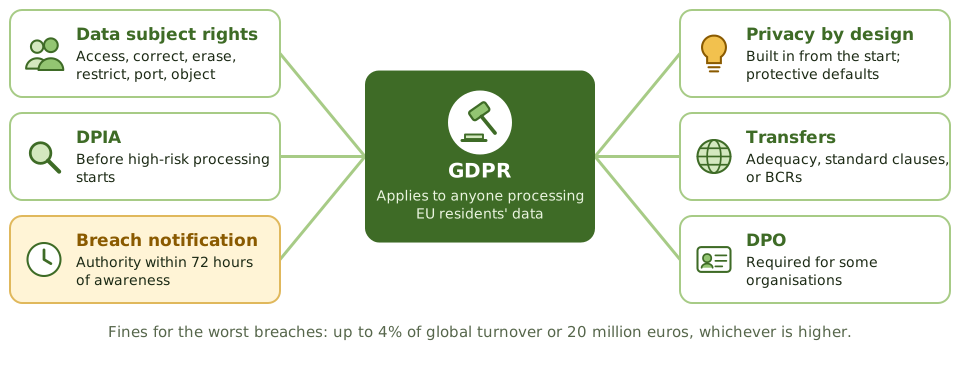
- Data subject rights: access, rectification, erasure (“right to be forgotten”), restriction, portability, objection, and rights about automated decision-making.
- Privacy by design and by default: built in from the start, with protective default settings.
- Data protection impact assessment (DPIA): required before processing that’s likely to be high-risk.
- Data protection officer (DPO): required for certain organisations.
- Breach notification: to the supervisory authority without undue delay and, where feasible, within 72 hours of becoming aware; to the individuals without undue delay if the risk to them is high.
- International transfers: only with an adequacy decision, standard contractual clauses, binding corporate rules or another approved mechanism.
- Fines: up to 4% of global annual turnover or €20 million, whichever is higher, for the most serious breaches.
Encryption reduces the impact of a breach, but it doesn’t replace the need for a lawful basis to process the data in the first place.
Other laws follow similar ideas: CCPA/CPRA in California, PIPEDA in Canada, LGPD in Brazil, DPDP in India, and HIPAA for US health data.
Auditing privacy
- Is there an inventory of personal data and records of processing?
- Is there a lawful basis and a privacy notice for each purpose?
- Were DPIAs done for high-risk processing?
- Are data subject requests handled within legal deadlines?
- Are retention periods defined and enforced?
- Are processors bound by contracts with appropriate terms?
- Can the breach response process meet notification deadlines?
- Are cross-border transfers covered by a legal mechanism?
Example. A mobile app asks for access to users’ contacts and location, though it only needs an email address to work. The data is encrypted and well protected. It still breaks data minimisation and purpose limitation, and probably transparency.
How the exam asks about it
| If the question asks… | The answer is usually… |
|---|---|
| Collecting more data than needed | Violates data minimisation |
| GDPR breach notification deadline to the authority | 72 hours after becoming aware |
| Party that decides purposes of processing | Controller |
| Assessment before high-risk processing | Data protection impact assessment |
| Who is accountable when a processor causes a breach | The controller (the processor may also be liable) |
| Difference between privacy and security | Privacy covers appropriate use; security covers protection |
In short
- Privacy is about the appropriate collection, use, sharing and retention of personal information; security is one of the means to protect it.
- Core principles: lawfulness, fairness and transparency; purpose limitation; data minimisation; accuracy; storage limitation; integrity and confidentiality; accountability.
- Under GDPR, the controller decides purposes and means; the processor processes data on the controller's behalf under contract.
- Data subjects have rights including access, rectification, erasure, restriction, portability and objection.
- Personal data breaches likely to result in risk must be reported to the supervisory authority within 72 hours of awareness.
- A data protection impact assessment (DPIA) is required for high-risk processing; privacy by design builds protection in from the start.
- Cross-border transfers need a legal mechanism, such as adequacy decisions or standard contractual clauses.
Exam traps
- Collecting more data than needed violates data minimisation, even if it's secured.
- The controller remains accountable even when a processor causes a breach.
- Encryption reduces breach impact but doesn't remove the need for a lawful basis.
- A privacy impact assessment is done before processing starts, not after.
- Privacy and security overlap but differ: a secure system can still violate privacy.
Slides
Click the slide and use the arrow keys. F toggles full screen.
Privacy isn't just security
A doctor's receptionist who locks your medical file in a safe has kept it secure. If they also asked for your salary and shared your details with a marketing firm, they've broken your privacy, however secure the safe was.
Privacy is about whether personal information should be collected, how it's used and shared, how long it's kept, and people's rights over it. Security is one of the tools that protects it.
The seven principles
Controller and processor
GDPR essentials