Topics in this domain
- IT Service Management
- Hardware Components and Architecture
- Operating Systems
- OSI Model
- TCP/IP and Common Protocols
- Network Devices: Switches, Routers, Gateways
- LAN/WAN Topologies
- Database Models and DBMS
- Database Controls and Normalization
- Asset Management
- Configuration Management
- Job Scheduling and Batch Processing
- Incident Management
- Problem Management
- Change Management
- Release and Patch Management
- Service Level Management
- Capacity and Performance Monitoring
- End-User Computing
- BCP Lifecycle
- Business Impact Analysis
- RTO, RPO, MTD, SDO
- Recovery Strategies
- Alternate Sites: Hot, Warm, Cold
- Backup Types: Full, Incremental, Differential
- Backup Storage and Rotation
- DRP Contents
- Testing BCP/DRP
- High Availability, RAID, Insurance
- Auditing BCP
Asset Management
You can’t protect what you don’t know about
Before you insure your home, you list what’s in it. If the expensive camera isn’t on the list, it isn’t covered when it’s stolen.
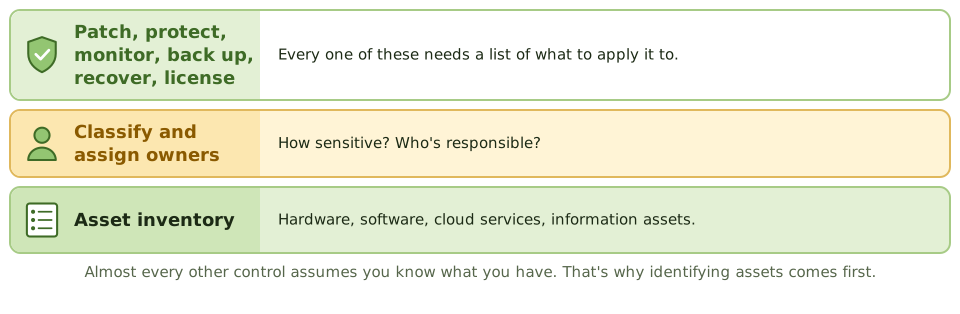
IT works the same way. You can’t patch, protect, back up, license or recover a server nobody knows exists. That’s why identifying assets is the first step in risk assessment, security programmes and continuity planning, and why unmanaged “shadow” assets are such a common finding.
What’s tracked
- Hardware: servers, laptops, network devices, mobile devices, storage media
- Software: installed applications and licences
- Cloud services: subscriptions, accounts, resources
- Information assets: key databases and data sets, usually with a classification
Each record should include an identifier, owner, custodian, location, classification, version or configuration, status, support and warranty details, and licence information. Assets without owners tend to go unpatched and unwatched.
The asset inventory (what you own) overlaps with the CMDB (how components are configured and connected), but they’re not the same thing.
From purchase to disposal
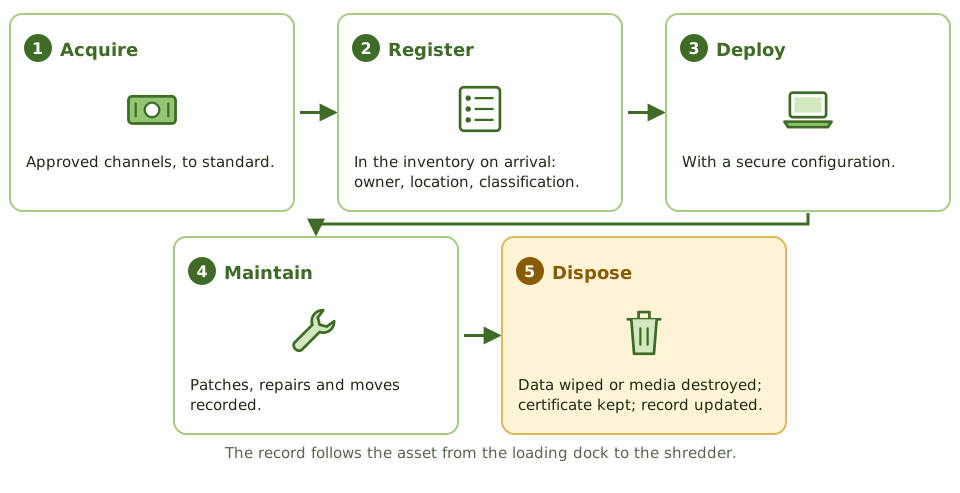
- Acquire through approved channels, to standard.
- Register in the inventory on arrival.
- Deploy with a secure configuration.
- Maintain: record patches, repairs and moves.
- Dispose: securely wipe data or destroy the media, keep a certificate or log, and update the record. Disposal without secure data destruction is a data breach waiting to happen.
Keeping the list honest
- automated discovery tools: network scans, endpoint agents, cloud APIs
- reconciliation between discovery results, purchase records and the inventory
- periodic physical checks of high-value or sensitive assets
- links with HR (leavers hand back equipment) and procurement (new purchases are registered)
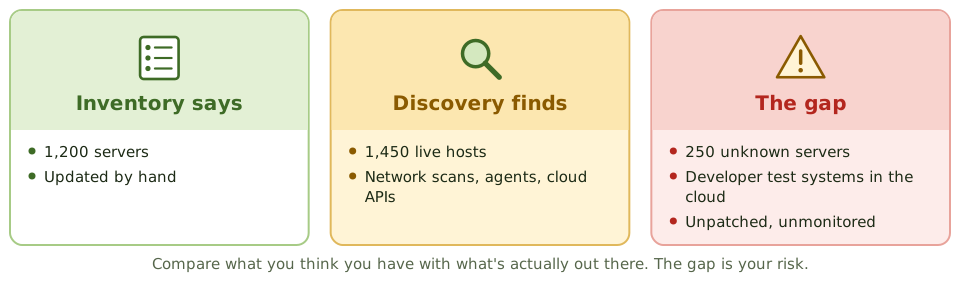
Example. A vulnerability scan covers the 1,200 servers listed in the inventory. Network discovery finds 1,450 live hosts. The 250 unknown servers include test systems developers built in the cloud, none of them patched or monitored. The root cause: an inventory that relies on manual updates.
Software licences
Software asset management compares licences owned with software actually installed and used. Too few licences creates legal and financial risk; too many wastes money. Restricting who can install software makes this much easier.
How the exam asks about it
| If the question asks… | The answer is usually… |
|---|---|
| First step in protecting information assets | Identify and inventory the assets (then classify them) |
| Best way to keep the inventory complete | Automated discovery reconciled to the inventory |
| Risk of assets without owners | Not patched, monitored or protected |
| Control before disposing of hardware | Secure data destruction, documented |
In short
- IT asset management maintains an accurate inventory of hardware, software, cloud services and information assets.
- You can't protect, patch, license or recover what you don't know you have; the inventory is foundational.
- Each asset should have an owner, location, classification, configuration details and life cycle status.
- Assets are managed through acquisition, deployment, maintenance, and secure disposal.
- Discovery tools and reconciliation against purchase records keep the inventory complete.
- Software asset management compares licences owned with software installed and used.
Exam traps
- The first step in many security and continuity programs is identifying assets.
- Assets without owners tend to go unpatched and unmonitored.
- Disposal without secure data destruction is a data breach risk.
- Asset inventory (what you own) differs from the CMDB (how components are configured and related), though they overlap.
Slides
Click the slide and use the arrow keys. F toggles full screen.
You can't protect what you don't know about
Before insuring your home, you list what's in it. If the expensive camera isn't on the list, it isn't covered when it's stolen.
IT works the same way. You can't patch, protect, back up, license or recover a server nobody knows exists. That's why identifying assets is the first step in risk assessment, security and continuity planning.
From purchase to disposal
Keeping the list honest