Topics in this domain
- IT Service Management
- Hardware Components and Architecture
- Operating Systems
- OSI Model
- TCP/IP and Common Protocols
- Network Devices: Switches, Routers, Gateways
- LAN/WAN Topologies
- Database Models and DBMS
- Database Controls and Normalization
- Asset Management
- Configuration Management
- Job Scheduling and Batch Processing
- Incident Management
- Problem Management
- Change Management
- Release and Patch Management
- Service Level Management
- Capacity and Performance Monitoring
- End-User Computing
- BCP Lifecycle
- Business Impact Analysis
- RTO, RPO, MTD, SDO
- Recovery Strategies
- Alternate Sites: Hot, Warm, Cold
- Backup Types: Full, Incremental, Differential
- Backup Storage and Rotation
- DRP Contents
- Testing BCP/DRP
- High Availability, RAID, Insurance
- Auditing BCP
Auditing BCP
Could they really recover?
A fire inspector doesn’t just read the fire safety manual. They check the extinguishers are charged, the exits are clear, and the staff know where to go.
Auditing business continuity is the same. The question is simple: could the organisation recover its critical processes within acceptable time and data loss if something went badly wrong? The plan document is only the start.
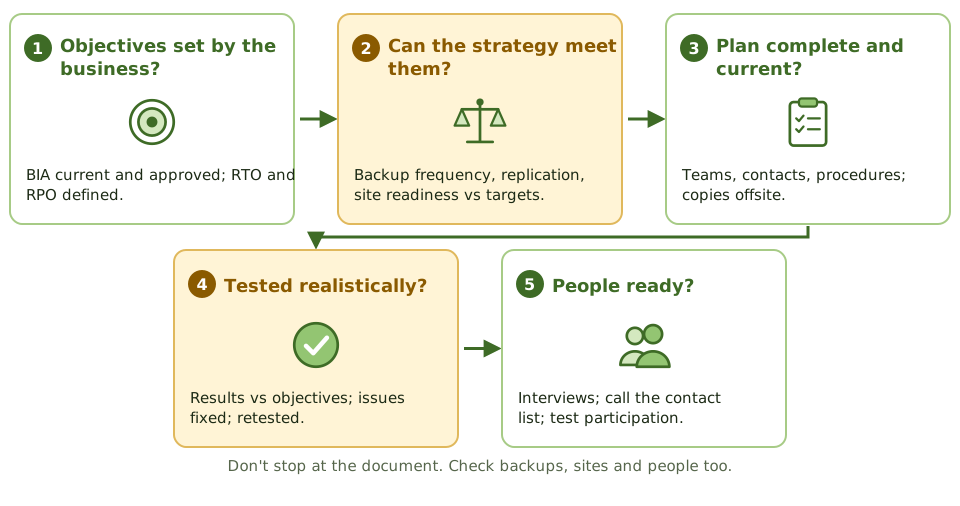
That breaks down into five questions:
- Are critical processes and recovery objectives identified and approved by the business? If not, the whole plan rests on IT’s assumptions.
- Can the recovery strategies actually meet those objectives?
- Are the plans complete, current and available?
- Have the plans been tested realistically, and were weaknesses fixed?
- Do people know their roles?
Procedures
Governance and the BIA
- Review the BCP policy, scope and responsibilities.
- Review the BIA: are critical processes, impacts and RTO/RPO identified, current and approved by senior management?
Strategy
- Compare each critical system’s RTO and RPO with what the strategy can really deliver: backup frequency, replication, site readiness.
- Read alternate site contracts: configuration, capacity, oversubscription, testing rights, duration.
- Check dependencies on cloud and other providers, and their own continuity arrangements.
Plans
- Check the BCP and DRP are complete: declaration, teams and backups, contacts, procedures, return to normal.
- Check they’re current, by comparing them with recent system, organisation and supplier changes. A plan not updated after big changes is likely to fail.
- Confirm copies are kept offsite and can be reached.
Testing
- Review the test schedule, scope and realism.
- Compare results with objectives: time to recover, data recovered.
- Confirm issues were tracked to resolution and the plan updated.
- Observe a test where possible.
Verification
- Reconcile the offsite backup inventory with backup records; visit or review the offsite facility.
- Review evidence of restore tests.
- Interview team members about their roles.
- Call a sample of numbers on the contact list.
- Compare insurance cover with the risks identified.
The auditor’s role
The auditor evaluates and reports. They may advise while the plan is being developed, but they don’t write or own it. That would impair their independence when they audit it later.
Example. An auditor finds a detailed DRP with 4-hour RTOs for core systems, approved last year. The last test was a tabletop exercise two years ago, and backup restores have never been timed. The auditor can’t conclude the 4-hour objective is achievable, and reports that the plan’s effectiveness hasn’t been demonstrated.
How the exam asks about it
| If the question asks… | The answer is usually… |
|---|---|
| Best evidence a DRP will work | Results of a realistic test |
| First item to review in a BCP audit | The BIA and recovery objectives (or the plan’s approval and currency) |
| Plan untested | Major finding; effectiveness not demonstrated |
| Most effective way to check staff readiness | Interview team members; review test participation |
| Verifying backups | Reconcile offsite inventory; review restore tests |
| Auditor asked to write the BCP | Advise only; ownership stays with management |
In short
- The auditor evaluates whether the BCP and DRP are adequate, current, tested and able to meet the business's recovery objectives.
- Start by understanding the BIA: are critical processes and recovery objectives identified and approved?
- Check that strategies (sites, backups, contracts) can actually meet the RTOs and RPOs.
- Review test plans and results: the best evidence that the plan works is a successful, realistic test.
- Verify offsite storage, backup inventories, copies of the plan, and alternate site contracts.
- Interview team members to check they know their roles, and check contact lists are current.
Exam traps
- A well-written plan that has never been tested gives little assurance.
- If the plan's recovery objectives weren't set by the business, the whole plan rests on IT assumptions.
- Reviewing the plan document alone isn't enough; verify backups, sites and people.
- The auditor evaluates and reports; the auditor doesn't write or own the plan.
- A plan not updated after major system changes is likely to fail.
Slides
Click the slide and use the arrow keys. F toggles full screen.
Five questions